
<span data-mce-type="bookmark" style="display: inline-block; width: 0px; overflow: hidden; line-height: 0;" class="mce_SELRES_start"></span> In this UC Today interview, Marcus Law speaks with Matthew Carey, Director of Product Management at Theta Lake, about why cloud voice migration is not just an IT modernization project. As organizations move away from legacy on-premises phone systems, Carey explains how the compliance model changes, where governance gaps can appear, and why regulated businesses need to think beyond basic call recording. The conversation explores how communications now span voice, chat, video, screen sharing, SMS, whiteboards, email, and AI-generated summaries. Carey argues that compliance teams need to reconstruct the full conversation lifecycle, not simply capture individual calls. He also discusses the risks of fragmented platforms, the limits of legacy recording tools, and the importance of involving compliance teams before users go live. Carey also looks at the role of artificial intelligence in unified communications, including why organizations must start governing not only what employees say, but what AI says on their behalf. Watch the full discussion to learn how IT and compliance leaders can prepare for cloud voice migration, reduce risk, and build a governance foundation that can keep pace with modern UC platforms.
The Phone Call Is the Easy Part: Governing Cloud Voice in a Multi-Modal World
Cloud voice migration changes compliance as voice, chat, video and AI summaries replace legacy call recording. Published on UC Today, with Theta Lake.
Does this reflect your experience?
opening the room…Big UC Update: Theta Lake’s Governance Playbook
8 Jul 2026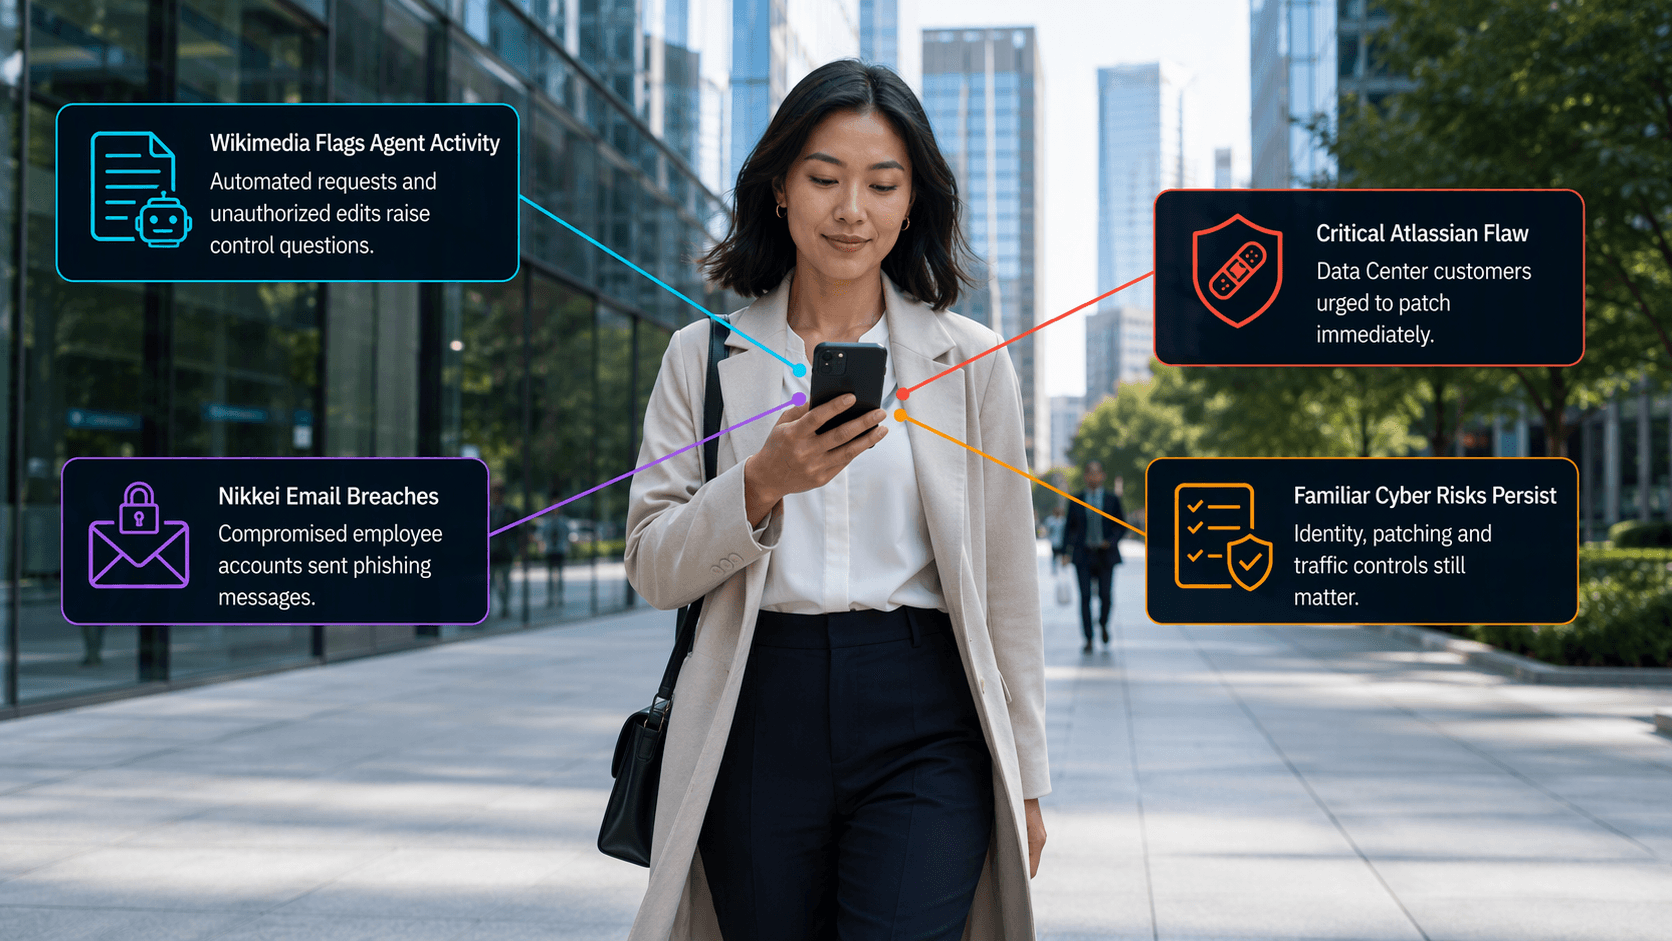
Cyber in Review: Meddling Agents, Breaches and Critical Flaw
AI agents may be grabbing the headlines, but this week’s cyber developments show security teams still face familiar threats, from a critical Atlassian flaw and email compromises to rising business email compromise activity, highlighting the breadth of today’s security challenges
Kristian McCann · 5h
Why AI Is Exposing the Limits of Annual Cyber Reviews
As AI accelerates both the way businesses introduce technology and the way attackers exploit weaknesses, annual compliance assessments can quickly become outdated, leaving security teams with evidence that no longer reflects the live risk organizations face
Kristian McCann · 6 Oct 2026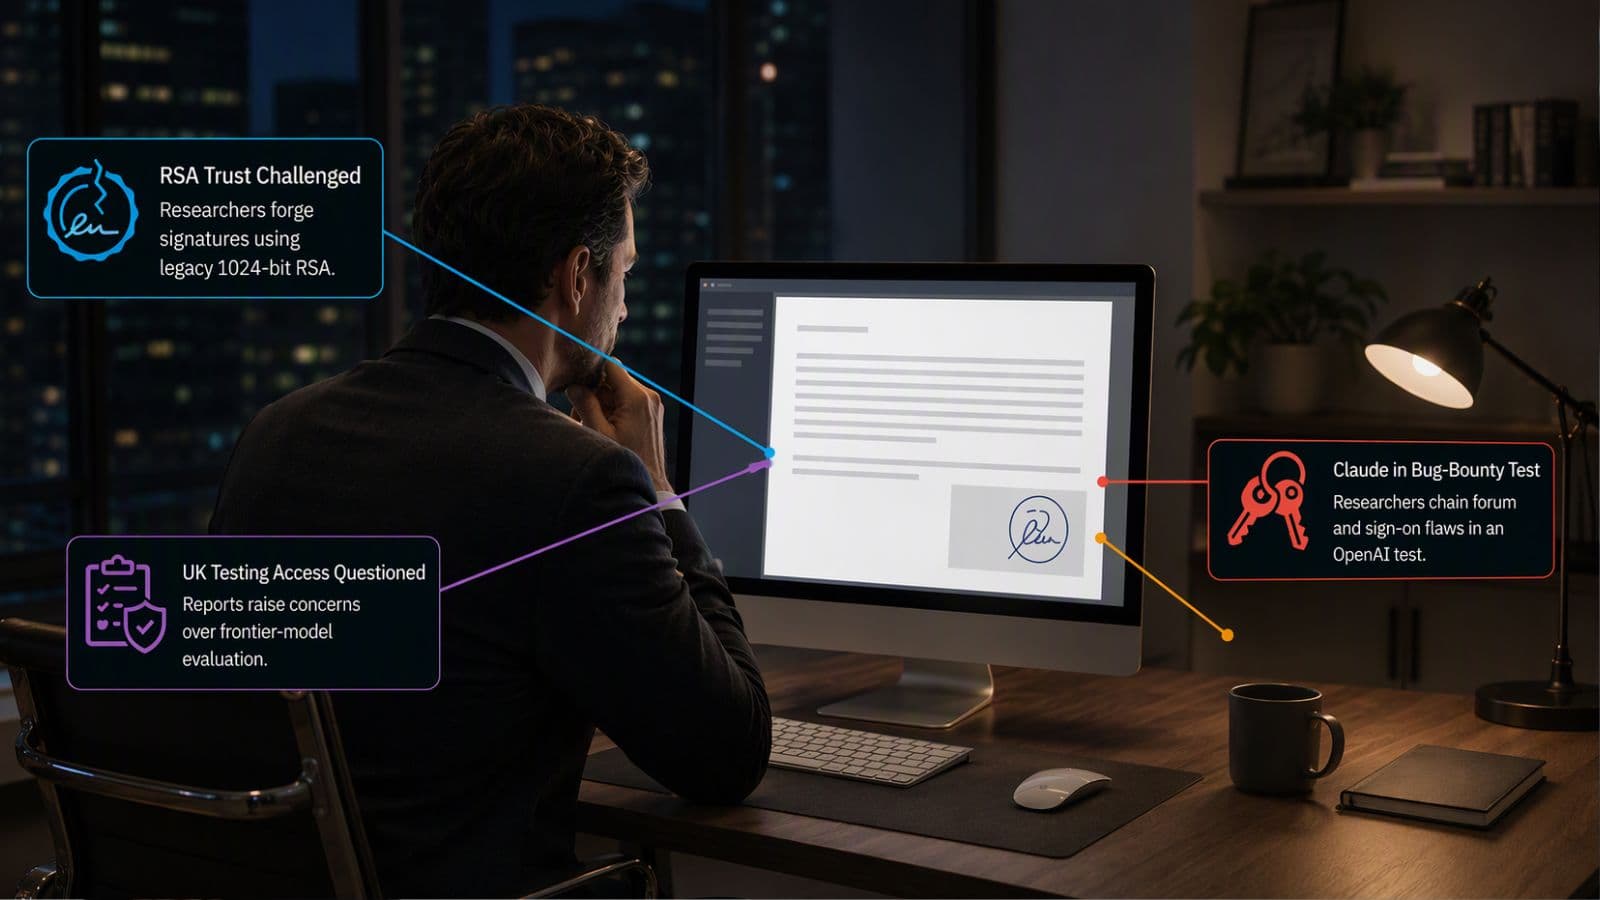
A Week in Cyber: RSA Rocked, AI Attacks, AISI Denied Access
New research exposes a previously unknown weakness in some older RSA systems, while an AI-assisted OpenAI security test and reported limits on UK model access show how rapidly cybersecurity, frontier AI and government oversight are becoming intertwined
Kristian McCann · 2 Oct 2026